Research at NetML

Where AI meets network security.

We build AI methods for network security and efficient language-model systems: detecting threats, identifying devices, reducing noisy features, and making retrieved context more useful to LLMs.

Our focus

Four connected research directions.

Our projects connect network measurement, optimization, and language models to practical problems.

Language models

Language Models, Security, and Privacy

We study language models for cybersecurity applications, including incident classification and adaptive honeypots, alongside retrieval-augmented generation, context optimization, privacy-preserving text anonymization, and efficient model architectures.

Related papers

Insight

Optimization and explainable AI

We reduce redundancy in high-dimensional security telemetry while preserving classification performance. Genetic algorithms, Artificial Bee Colony optimization, feature selection, quantization, and SHAP help us refine models and explain their decisions.

Related papers

Selected research

Methods tested on real research problems.

Four studies show how the lab works across efficient language models, cyber deception, device identification, and network threat detection.

Long-context AI · 2026

Jointly pruning RAG context

JMAP: Joint Multi-Document Attention with Clustering-Based Adaptive Context Pruning for Retrieval-Augmented Generation

A 149M-parameter ModernBERT-base cross-encoder scores sentences across retrieved documents in one 8,192-token pass. Clustering sets an adaptive threshold to preserve evidence while removing distracting text.

On HotpotQA, 2WikiMultihopQA, MuSiQue, and TriviaQA, pruned context improved Qwen3-8B answer F1 over unpruned context in the paper's evaluation.

81–87%of context tokens removed, with a reported 1.24–1.45× end-to-end speedup.
View publication details

Adaptive cyber deception · 2026

LLM-driven web honeypots

An LLM-Driven Adaptive Honeypot Testbed for Dynamic Intrusion Engagement

This healthcare-domain prototype generates context-aware pages from a pool of LLMs. Semantic checks keep responses consistent as an interaction unfolds, targeting manual exploration and post-exploitation rather than automated reconnaissance.

Graduate researchers tested benign and adversarial interactions in controlled Chameleon Cloud simulations to examine feasibility, interaction depth, and content quality.

Controlled prototypeInternal red-team scenarios tested the architecture; the study did not use internet-scale attacker traffic.
View publication details

IoT identification · 2025

Explainable IoT fingerprinting

Automated IoT Fingerprinting with LLMs: Harnessing Explainable AI and Artificial Bee Colony Optimization

The method analyzes network packets, then uses SHAP and Artificial Bee Colony optimization to select relevant features before an LLM classifies IoT devices.

Up to 75%fewer packet features, with up to 98.9% classification accuracy in the reported experiments.
View publication details

Network threat detection · 2024

Automated incident identification

Automated Network Incident Identification through Genetic Algorithm-Driven Feature Selection

Genetic algorithms select packet-level features for machine-learning detection of DNS botnets, Nmap OS scanning, and DoS HULK and GoldenEye attacks without manual feature selection.

Mid-95% / 100%Accuracy in the paper's datasets: mid-95% for Nmap scanning and DNS botnets; 100% for DoS HULK and GoldenEye.
View publication details
Current studies

Ongoing Research

Current studies in explainable network analysis and privacy-preserving language models.

Ongoing Research

Explainability-Guided Feature Reduction for Network Incident Classification: A Comparative Study of Deep Learning and Large Language Models

This study combines SHAP and LIME feature attribution with Artificial Bee Colony optimization to identify informative network traffic features. It compares deep learning and large language models for classification performance, feature efficiency, and interpretability.

Ongoing Research

Fast Span-Constrained Text Anonymization with Masked Diffusion Language Models

This study uses masked diffusion language models to rewrite privacy-sensitive spans while preserving the surrounding text. It aims to improve editing efficiency, content preservation, and privacy protection.

Selected projects

Research tools from the lab.

Open-source frameworks make our methods available for others to explore and extend.

Open-source research framework

AutoIC

Automated network traffic analysis and feature optimization

AutoIC is an open-source framework for automated network traffic analysis and machine-learning-based incident detection. It uses genetic algorithms for feature selection and SHAP and LIME to explain which traffic features influence predictions.

Future researchBehavioral fingerprinting, adaptive detection, and incremental learning are potential future directions.
Explore AutoIC on GitHub

Research appearances

Explore the work beyond our papers.

An interview, presentation, and features from UCM Magazine and Chameleon Cloud share the ideas behind our research.

Research interview

A conversation on cybersecurity research and the lab's interdisciplinary approach.

Fast-flux detection presentation

Machine learning and genetic algorithms for detecting fast-flux networks.

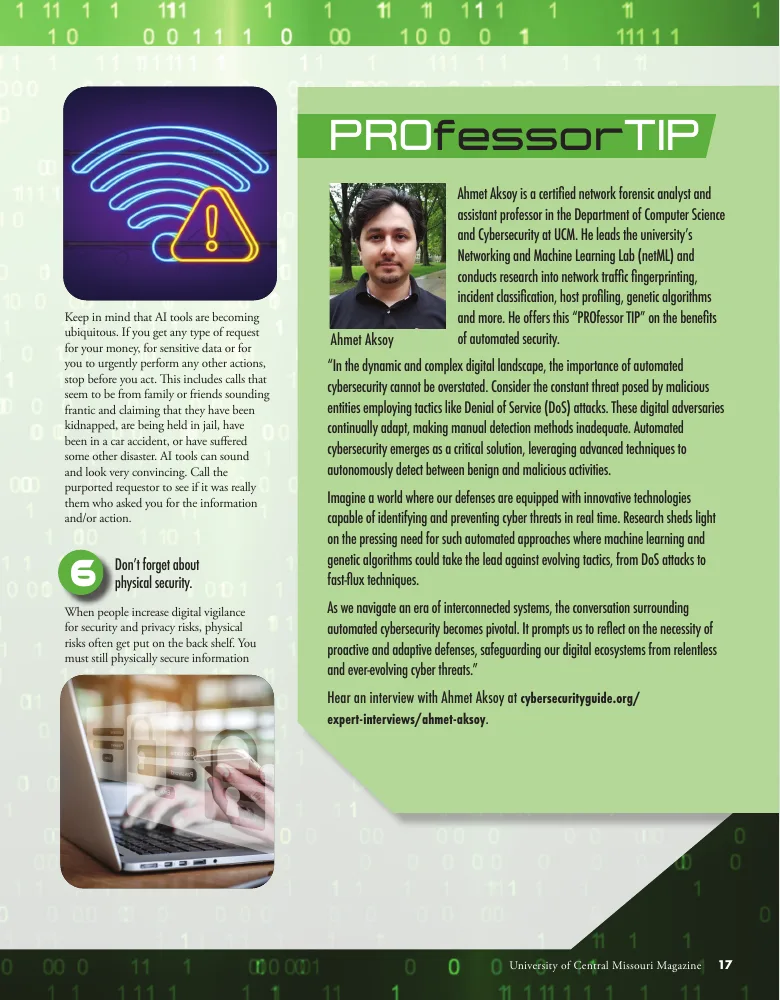
Spring 2024 UCM Magazine page featuring Dr. Aksoy on automated cybersecurity

Featured in UCM Magazine

Spring 2024 · Page 17

Dr. Aksoy discusses automated cybersecurity and how machine learning and genetic algorithms can help identify evolving network threats.

Read the magazine feature (PDF)

Collaborate

Interested in working with NetML?

We welcome students and collaborators interested in machine learning, LLMs, networking, and cybersecurity.

Get in touch